Regulation and markets
A regulatory requirement first reads as a constraint. It often reveals an architecture flaw, such as a misplaced control or an unclear responsibility.
We turn the requirement into an operating set-up, taking into account the tension between Luxembourg obligations and group directives.
Typical situations
- DORA compliance: ICT risk, third-party providers, resilience.
- Solvency II reporting and governance in an insurance subsidiary.
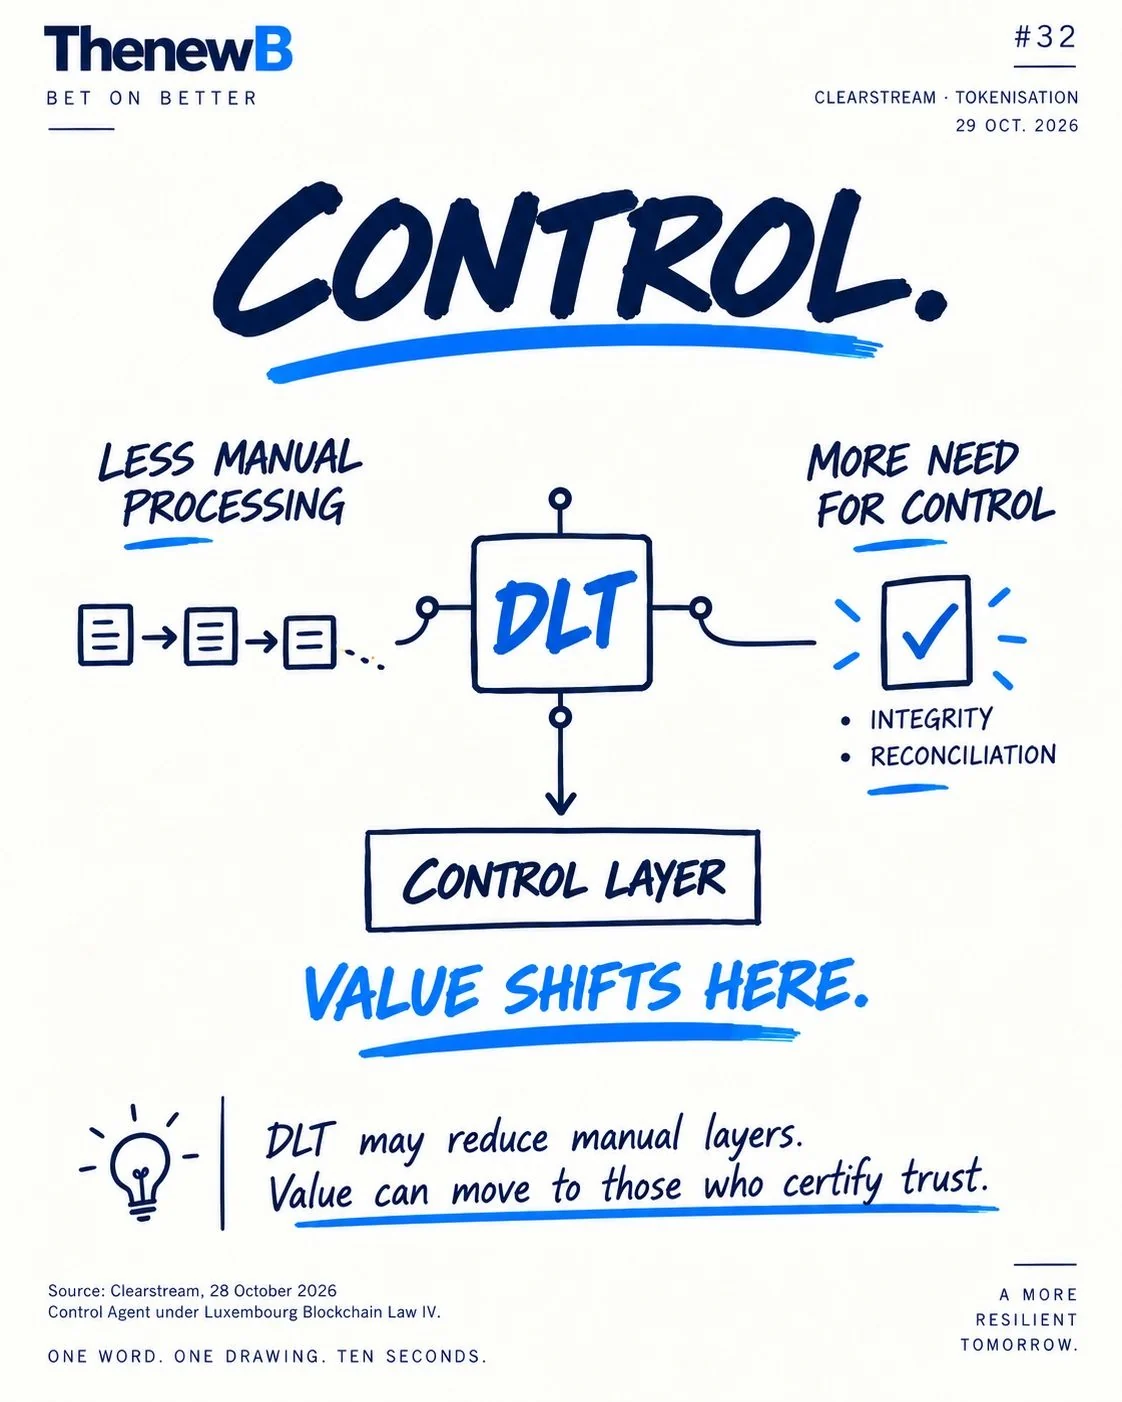
- New market obligations, from MiFID II to tokenisation.
- A group directive to apply without contradicting a CSSF or CAA expectation.
How we work
- 01
Read the requirement
Separate what is mandatory, what is expected and what is a matter of interpretation.
- 02
Redesign the set-up
Build the requirement into the controls, responsibilities and data of day-to-day operations.
- 03
Reconcile local and group
Document the gaps and have them decided at the right level.
Ready to think differently?
Talk to us